Security Considerations for Gotenberg API in Document Conversion Services
Exploring the security implications and best practices for using Gotenberg's API in document conversion workflows
CANADA — Gotenberg, an API service designed for document conversion, presents unique security challenges due to its lack of a user interface. Unlike traditional web services, Gotenberg's minimal UI means that exposure measurements require careful interpretation, as a public instance might appear as a simple web page while still capable of processing files and fetching remote URLs.
Recent measurements revealed 3,971 matches for app="Gotenberg", highlighting the service's widespread use. However, the security implications are significant: while the API supports basic authentication and OIDC, these measures alone don't prevent the submission of untrusted documents or URLs that could access internal services. This separation between request authorization and document trust necessitates additional security layers.
Security experts recommend several best practices for Gotenberg deployments. Services should be kept behind trusted backends and off public networks. Configuration should include strict upload limits, timeouts, and carefully controlled outbound destinations. Additionally, testing should verify that the service blocks private address resolutions and malformed documents that might expose system files.
For optimal security, Gotenberg should run in dedicated containers with read-only file systems when possible. Network egress should be restricted to only necessary document sources, and separate worker instances should handle different document types (HTML, office documents, PDFs) when their resource needs differ. Regular patching of both the service and its bundled engines is critical.
The unique nature of Gotenberg's API means that traditional security assessments may not fully capture its exposure risks. Developers should approach the 3,971 identified instances as potential services requiring verification rather than as confirmed, properly configured endpoints. This approach is particularly important given Gotenberg's ability to process documents and make network requests.
Reported with files from DEV Community.
 News
Ollama Local LLM Gains Monitoring Tools for Production Use
Developers adopting Ollama for local LLM deployment now have guidance on monitoring metrics, logs, and traces as usage scales beyond personal projects.
 News
GitHub Merge Queue Test Shows Tradeoffs for AI Coding Agent Workflows
Benchmark reveals merge queues eliminate rejected pushes but add latency when coordinating multiple AI agents on a single codebase
 News
Developers Can Improve Online Presence with Person Schema and Wikidata
A software developer shares practical steps to help Google connect disparate online profiles into a unified knowledge panel.
 News
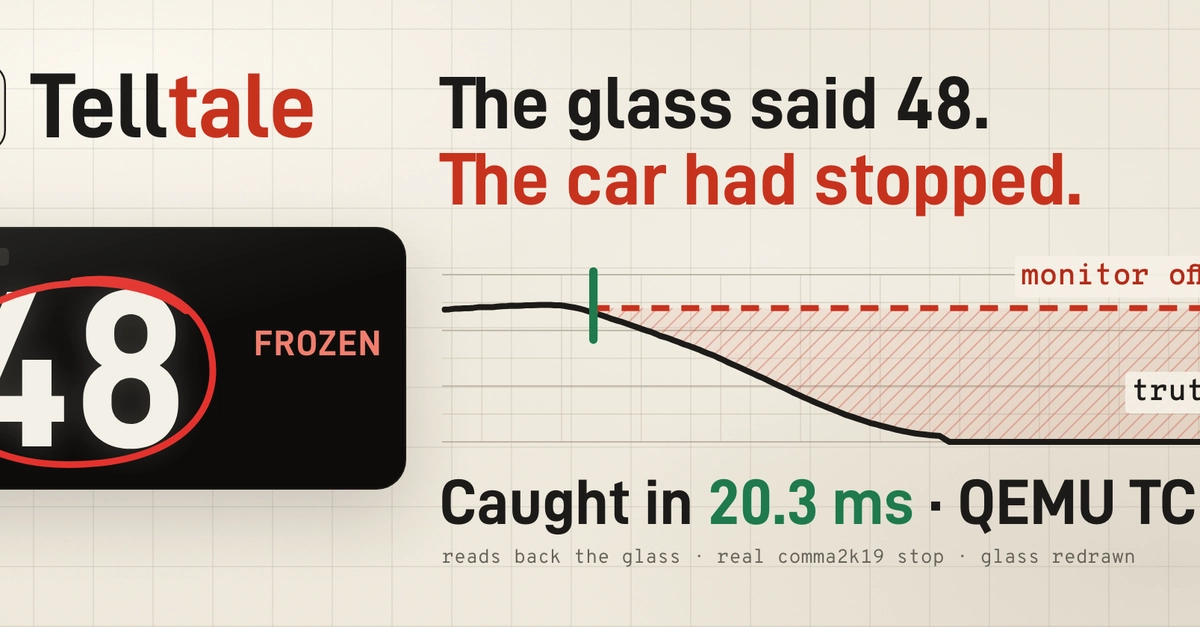
QNX 8.0 Tool 'Telltale' Detects False Instrument Reads in Real-Time
Open-source monitor verifies automotive display accuracy by reading back pixels, addressing critical safety gaps in renderer processes